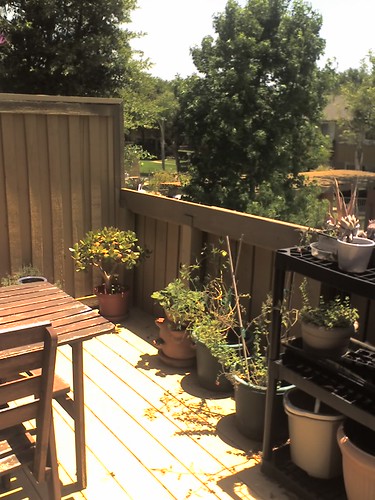
06-16-07_1338.jpg, originally uploaded by Kelson.

This is a picture I took last summer of the balcony on our old apartment. I used it to test using Flickr’s email upload and blog-posting features to upload a picture straight from my phone.

Unfortunately, it needed cleanup. The title (and post slug) end up being the filename, which I suppose I can fix before sending, and the content seems to get posted twice. I suspect the phone is sending both formatted and plain-text versions of the message, and Flickr is reading them both.

Anyway, it’s not a bad picture, so I figured I’d leave it up instead of deleting the test post.

Bart Allen as the FlashI’ve just launched SpeedForce.org, a companion blog to the website, Flash: Those Who Ride the Lightning.

Since I started adding news items to the front page of Ride the Lightning, it’s started to get a bit crowded. I thought about converting it to a Delicious feed, but then I realized it really ought to be a blog. There hasn’t been a major Flash-focused blog out there since Crimson Lightning shut down, so I figured I’d step in and fill the gap. And I could use the domain I picked up last year!

I’ll be posting Flash-related news there, including a weekly round-up of Flash comics, as well as articles that might not fit into the existing site structure, and (eventually) reviews as well. Some stuff that I would have posted here will end up on the new site. Certainly Flash news, but I may start shifting more comics-related commentary over there as well.

I’ll be refining the look and features over the next couple of weeks, and cross-linking it more into Ride the Lightning. I might keep the current theme with a few tweaks, or I might try to match Ride the Lightning, or I might build something else entirely.

So please, check it out and let me know what you think! I’m open to suggestions as to content, design, etc. And of course bug reports.

Since Gravatar was bought by Automattic, the service has been a lot more stable. I had already re-enabled them on this blog before WordPress 2.5 came out with built-in Gravatar* support.

Not everyone has a Gravatar, though, so many comment threads just show the default icon, over and over. Not only does this look boring, but it misses out on the whole point of using an avatar: providing an easy at-a-glance visual distinction between each author.

When I first used Gravatars on this site, I set it up to use a giant first initial as a fallback. Now, I’ve been trying out two plugins that will automatically generate avatars for people who don’t have their own:

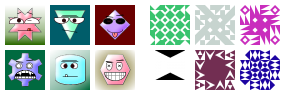
  • Wavatars builds up cartoony faces using geometric shapes. Interestingly, it’s by Shamus Young, author of the screencap-based webcomic DM of the Rings and writer of Chainmail Bikini.
  • WP_Identicon sounds like a Transformers faction, but produces a geometric pattern as inspired by Don Park’s Identicon, which built a similar image based on a visitor’s IP address. The same author also has one that generates cartoon monsters, which appears to be one of the earliest implementations of this concept.

These plugins will use a Gravatar if available, or else generate an image based on the commenter’s email address (if supplied). That means each comment by the same person should use the same image. Other blogs using the same plugins at default settings will come up with the same avatar for each commenter, as well. The images are stored in a cache, so each only has to be generated once.

6 Wavatars to the left, 6 Identicons to the right

Once I made sure both plugins worked, I showed the results to Katie. We ended up settling on Wavatars, since faces are easier to recognize than patterns. (Though the patterns are really cool!)

You can try out the automatic avatar by leaving a (relevant, please!) comment on any post. Or you can run over to Gravatar and set up an icon of your choice!

*What’s a Gravatar? The intent is to be a Globally Recognized Avatar. You upload an image to Gravatar and associate it with your email address. Then any site with Gravatar support will be able to display your image next to your posts. Right now it’s mostly used in blog comments, but it could easily be worked into forums, wikis, etc. The Gravatar Blog mentions other uses they’ve seen people apply it to, such as plugins for Thunderbird and the Mac OS X Address Book

Note: I did notice one important drawback to the WP_Identicon plugin: it’s very inefficient at generating the images. When I first visited posts with long comment threads, like Another One Bites the Dust (174 comments) and Songs Not to Play at a Wedding (87 comments), WP_Identicon took over a minute to generate all the icons and maxed out the server’s CPU. Sure, the images are cached, so it’s only really an issue when you first install the plugin (unless you get a lot more people commenting at once than we do here), but to compare, Wavatar on an empty cache finished the same posts in just 4 seconds and 2 seconds, respectively.

With bloggers squashing obviously-spammy links* as fast as they can, comment spammers have evolved. (I think they’ve reached the level of slime mold now, rather than amoebas.) They’re trying to make their sites look like blogs. And I’m seeing two main techniques, one involving Trackbacks/Pingbacks, the other involving manual person-at-a-keyboard commenting.

Misusing Pingbacks and Trackbacks

Pingbacks and Trackbacks are two ways for one site to notify another that it’s linked to it, and provide an excerpt of the context. Essentially, they’re automated comments. You read a post on some other site, you write your own response, linking to the original post, and your blog software submits the equivalent of “Hi, I read your post, and it got me thinking. I ended up writing my own post over here…”

Where spam is concerned, the main difference is that with Trackbacks, the submitting site provides an exceprt, but with Pingbacks, all it submits is the URL. The receiving blog then retrieves the page and scans it for the link, building an excerpt from the context. The upshot of this is that Pingbacks automatically verify that yes, the site really did link to you, which meant that a lot of early comment spam was submitted using Trackbacks.

The obvious response to that was to set up spam protection to verify links on incoming Trackbacks. And the obvious response by the spammers was to put up real links, at least long enough to let the victims verify them.

So now, a lot of trackback/pingback spam seems to come from sites running actual blogging software, but not really posting any content. Just “So-and so wrote an interesting post today” over and over, hundreds of times a day. Half the time they don’t bother to match the name to the actual link. This is the kind of spam that prompted my recent re-evaluation of spam plugins on this site.

Sneaky Intermediary

Then there was the sneaky post I got on Thursday. It was a sort-of half-on-topic comment on a post about movies, and the author’s URL pointed to what appeared to be a blog about movies. OK, fair enough, but I was still a bit suspicious since it didn’t look like they’d actually read my post.

I skimmed the site looking for things like cobbled-together sentences, and an idea of how long it had been around. Then there was a random post about guitars, in a different writing style. I figured, okay, maybe they’re doing one of those paid-post things.

Then I moved the mouse cursor over one of the links.

It quickly became clear that every single outgoing link on the front page was pointing to ultimate – free – downloads – dot – com, whether it was a movie title, or an actor, or a song title.

At this point I’m not sure whether the site in question is simply an elaborately designed intermediary created to “launder” the links to spam sites, or whether it’s a legit blog that’s been hijacked by someone replacing their links. I looked around at some of the older posts and I do see links to Amazon and a couple of other sites.

*This is also why I’ve stopped using the Alternative Browser Alliance as my URL when commenting on browser-related blogs. Even though I’m making an on-topic comment, I don’t want people to take a look at the link, say, “Hey, this isn’t a person, this is some weird campaign thing!” and delete the comment…and worse, get a rep as a comment spammer. So these days I just link everything here.

I just realized that as of last week, this blog has been online for 5 years.

Crazy, huh?

This is the 1,398th post. We’ve got 2,307 comments at the moment, including pingbacks. Typical traffic these days seems to run around 650-700 views on weekdays, 550-600 on weekends. Most of it seems to be people searching for images.

The top-viewed posts lately have been:

  1. Songs Not to Play at a Wedding (Normally #2, but it got something like 3000 hits from StumbleUpon last week.)
  2. Comic Con 2003
  3. Philosophy of Time Travel
  4. Creative Computer Names

Judging by a quartet of comments posted this evening, 3 of which slipped past Spam Karma, someone’s started outsourcing comment spam to India. (I’m serious, the IP addresses were assigned to Bharti Airtel and BSNL Internet, both ISPs based in New Delhi.)

They were posted quickly, as if they’d been composed in another editor and pasted into the form. More importantly, they were actually posted through the form, not just sending data directly to the handler. And most tellingly, the posters had gone to the effort to fill out the CAPTCHA that Spam Karma provides to allow human commenters to recover from a false positive.

The one I liked best, from a technical perspective, was posted on Tall Ships of San Diego. The spammer had followed my link to the San Diego Maritime Museum, then followed that to a page describing one of the ships, the Californian, and generated a post by stringing together sentences from that page. The whole thing linked to a student loan site.

At first glance, it looked like a garbled, on-topic comment from someone who maybe didn’t speak English as their first language. That happens, and if it’s a legit comment, I leave it. In fact, I considered leaving the comment but deleting the author URL, until I looked up the ship. (It wasn’t one of the ships we toured on our visit, and I didn’t recognize the name.) As I looked at the ship’s profile, I started recognizing text from the comment. At that point it became clear what was going on, and I started looking at the other comments posted over the last few hours.

Figured what the heck. I’m now on ComicSpace.

Because I need yet another site to suck up all my time.

It’s being described as MySpace for comics people—creators, fans, reviewers, etc.—though the feature set is pretty sparse right now. I’ve resisted MySpace itself partly because of a somewhat adversarial relationship with the site*, partly because I can’t stand looking at most MySpace pages, and partly because my friends are all on LiveJournal, so there’s really no compelling reason for me to go there.

And yet I’ve got profiles at LiveJournal, Slashdot, Opera, WordPress, Spread Firefox… Even eBay is adding blogging capabilities. Maybe I should bite the bullet and sign up for a Blogger account too. At least then I’ll be able to comment on Crimson Lightning.

*The culture at MySpace seems to encourage hotlinking images without asking. I’m still a writer at heart, so I consider the commentary to be as important as the images or more… and it really annoys me when people en masse just embed the images on their own site. Though I suppose it’s not as bad as the occasional “geniuses” on other forums who will hotlink an 800×600 or bigger photograph as their avatar, even though it only displays at 80×80. Damn kids, get off my lawn!

ยปAll pages site-wide with this tag