I’ve seen my share of angry complaints about spam with forged sender addresses, but this is amazing: Aunty Spam’s Slam a Spammer Blog is reporting that Sunnyvale resident Charles Booher called up the “sender” of some spam and threatened him with torture and death.

Of course, (a) death threats are criminal, and (b) the callee was not the actual sender but a third party whose address had been forged. Booher is now facing criminal charges with up to five years of prison and a quarter-million dollars in fines.

“Aunty Spam” didn’t provide any further information, but a quick Google search turned up articles suggesting this isn’t the entire story. Mercury News reports [archive.org] that the person Booher threatened, Douglas Mackay, worked at a call center that handled calls for, among other companies, the one that did send the spam. Metroactive reports on an even closer connection: it seems that the spamming corporation was registered to Mackay’s brother. A DOJ press release is (appropriately) matter-of-fact about the allegations. This all went down last November. In my brief search I haven’t found anything about the current status of the case.

Back on the subject of forgery, the SPF website has gotten a major facelift. SPF, or Sender Policy Framework, is a scheme that lets domain name owners identify which servers they use to send mail, so that receiving servers can pre-screen incoming mail for forgeries. Aside from cutting down on phishing attacks, at least with SPF there’s a better chance you’ll be complaining to the right person!

All the Linux desktop action these days is in KDE and GNOME, but on older hardware, servers, or anything else where you need to squeeze every last ounce of performance from the box, something lighter is needed.
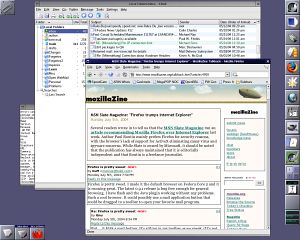
[Screenshot of a WindowMaker desktop] My Linux box at work — a 300 MHz Pentium II — runs WindowMaker. It’s familiar, it stays out of the way, and it doesn’t tie up the memory or CPU that a modern version of KDE or Gnome (or Windows, for that matter) would. But you need to add applets like a clock or a desktop pager. You can find them easily enough — I ended up using the aptly-named wmclock and wmpager – but there’s a significant problem with both. WindowMaker lets you change the size of the dock icons, but when I shrank the dock to get more space I discovered that both applets have a hard-coded size of 64×64 pixels.
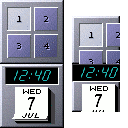
[Pair of WM Applets, first at default 64x64 size (they look fine), then at 48x48 (they don't adjust and edges get cut off)] As you can see, a 64×64 applet just doesn’t work in a 48×48 space. It surprised me, though, since these dockapps are designed specifically for WindowMaker, and it’s WindowMaker itself that lets you change the size. You open up Preferences, change the size, and restart WM. Just menus and buttons. No config files, no registry, no third-party add-on. This isn’t an esoteric hack that takes serious effort to find, it’s a basic feature. You might as well design a Mac program that assumes the Dock is on the bottom of the screen. For most people it will be, but it’s not rocket science to move it.

In my ICS classes, they always discouraged us from using “magic numbers” — just throwing a number in the code without identifying or abstracting it. There are two very good reasons for this. The first is that you might forget what this 64 is doing. The second is that you might decide to change it later on, and it’s much easier to change one SIZE=64 definition than to track down every 64 and hope you’ve neither missed any you need to change nor changed any you need to leave alone.

Those dock applets are stuck at 64×64 pixels because the programmers were thinking in terms of the pixel grid, not in terms of actual display size. Continue reading →

Here are several humor articles that have been posted to the SpamAssassin discussion list over the past week:

The TechWeb Spin: All spam is true! (Fredric Paul, Internet Week, June 29, 2004): Yes, you read it here: it’s all true! The author explains about all the money he’s gotten from deposed Nigerian dictators, the software discounts, the combined advantages of certain pharmaceuticals and dating services, and more! [Edit: Sadly the article was deleted before the Internet Archive got to it.]

It’s true, I read it on the Net! (author unknown): I remember seeing this way back when, under the title “The Ultimate Chain Letter.” It’s kind of like the parody of the Good Times Virus (remember that one?) in that it combines everything. All the urban legends about stolen kidneys, rats at KFC, needles in pay phones, and satanic business leaders. All the email hoaxes about Bill Gates giving you money and dying kids asking for email. All the typical chain letter threats about not breaking the chain.

Spam is out of this world (Adam Turner, Syndey Morning Herald, April 1, 2004): An April Fools’ piece about the Mars Spirit rover being crippled by spam traffic: “The rover’s limited onboard artificial intelligence was foolish enough to apply for an shonky online marketing diploma. Soon after offers of cheap WD40 and antenna enlargements began clogging the link between Mars and NASA’s Deep Space Network.” It goes on to explain that Beagle was taken down by a Martian Nigerian scam.

Welcome to Spam University: a parody of a school site with ridiculously low entry requirements (At least four years of elementary school, No more than three felony convictions), course descriptions (Harvesting Addresses, Covering Your Tracks, Spamming Ethics – Canceled), alumni testimonials and more!

To be honest, I haven’t used any instant messaging system much since college. But every once in a while I fire up Gaim just to see if anyone I know is on AIM or ICQ. I have a Yahoo account, but I’m not sure anyone I know actually uses Yahoo Messenger, and I’ve been avoiding MSN mainly on principle.

Sadly, it seems the IM wars have returned.

This time it’s Yahoo that’s blocked other clients from connecting to their networks. The most high-profile victim has been Trillian, another client which talks to multiple IM networks, but of course Gaim was hit as well. What’s interesting, this time, is that Yahoo claims it’s doing this to cut down on spam.

Now let’s think about this: In order to send and receive instant messages on Yahoo’s network, you need a Yahoo account, correct? So no matter what software a spammer uses to connect, he still needs to log in, which means Yahoo can control them inside the network. This is where current IM systems are fundamentally different from email: instead of many independently-controlled systems talking to each other, each IM service is one system with many accounts, more like a website with required registration. Place limits on what clients can do, and (barring bugs in your server) no matter what client someone uses, he can’t get around your spam/virus/hack controls.
Continue reading →

Long story short: while Eudora is still my favorite Windows-based email program, its HTML rendering is so bad that I had to read today’s Microsoft Technet newsletter on my Linux box. (And before anyone comments that I can set Eudora to use IE’s rendering engine, I don’t want the security mess of letting Internet Explorer handle my email.)

ยปAll pages site-wide with this tag